Catch fraud and errors before the payment, not after.
Fiatto records who may approve what, shows which permissions should not sit with one person and flags suspicious patterns, such as a bank account changed just before a payment. A person reviews the signal before release.
Included from Core
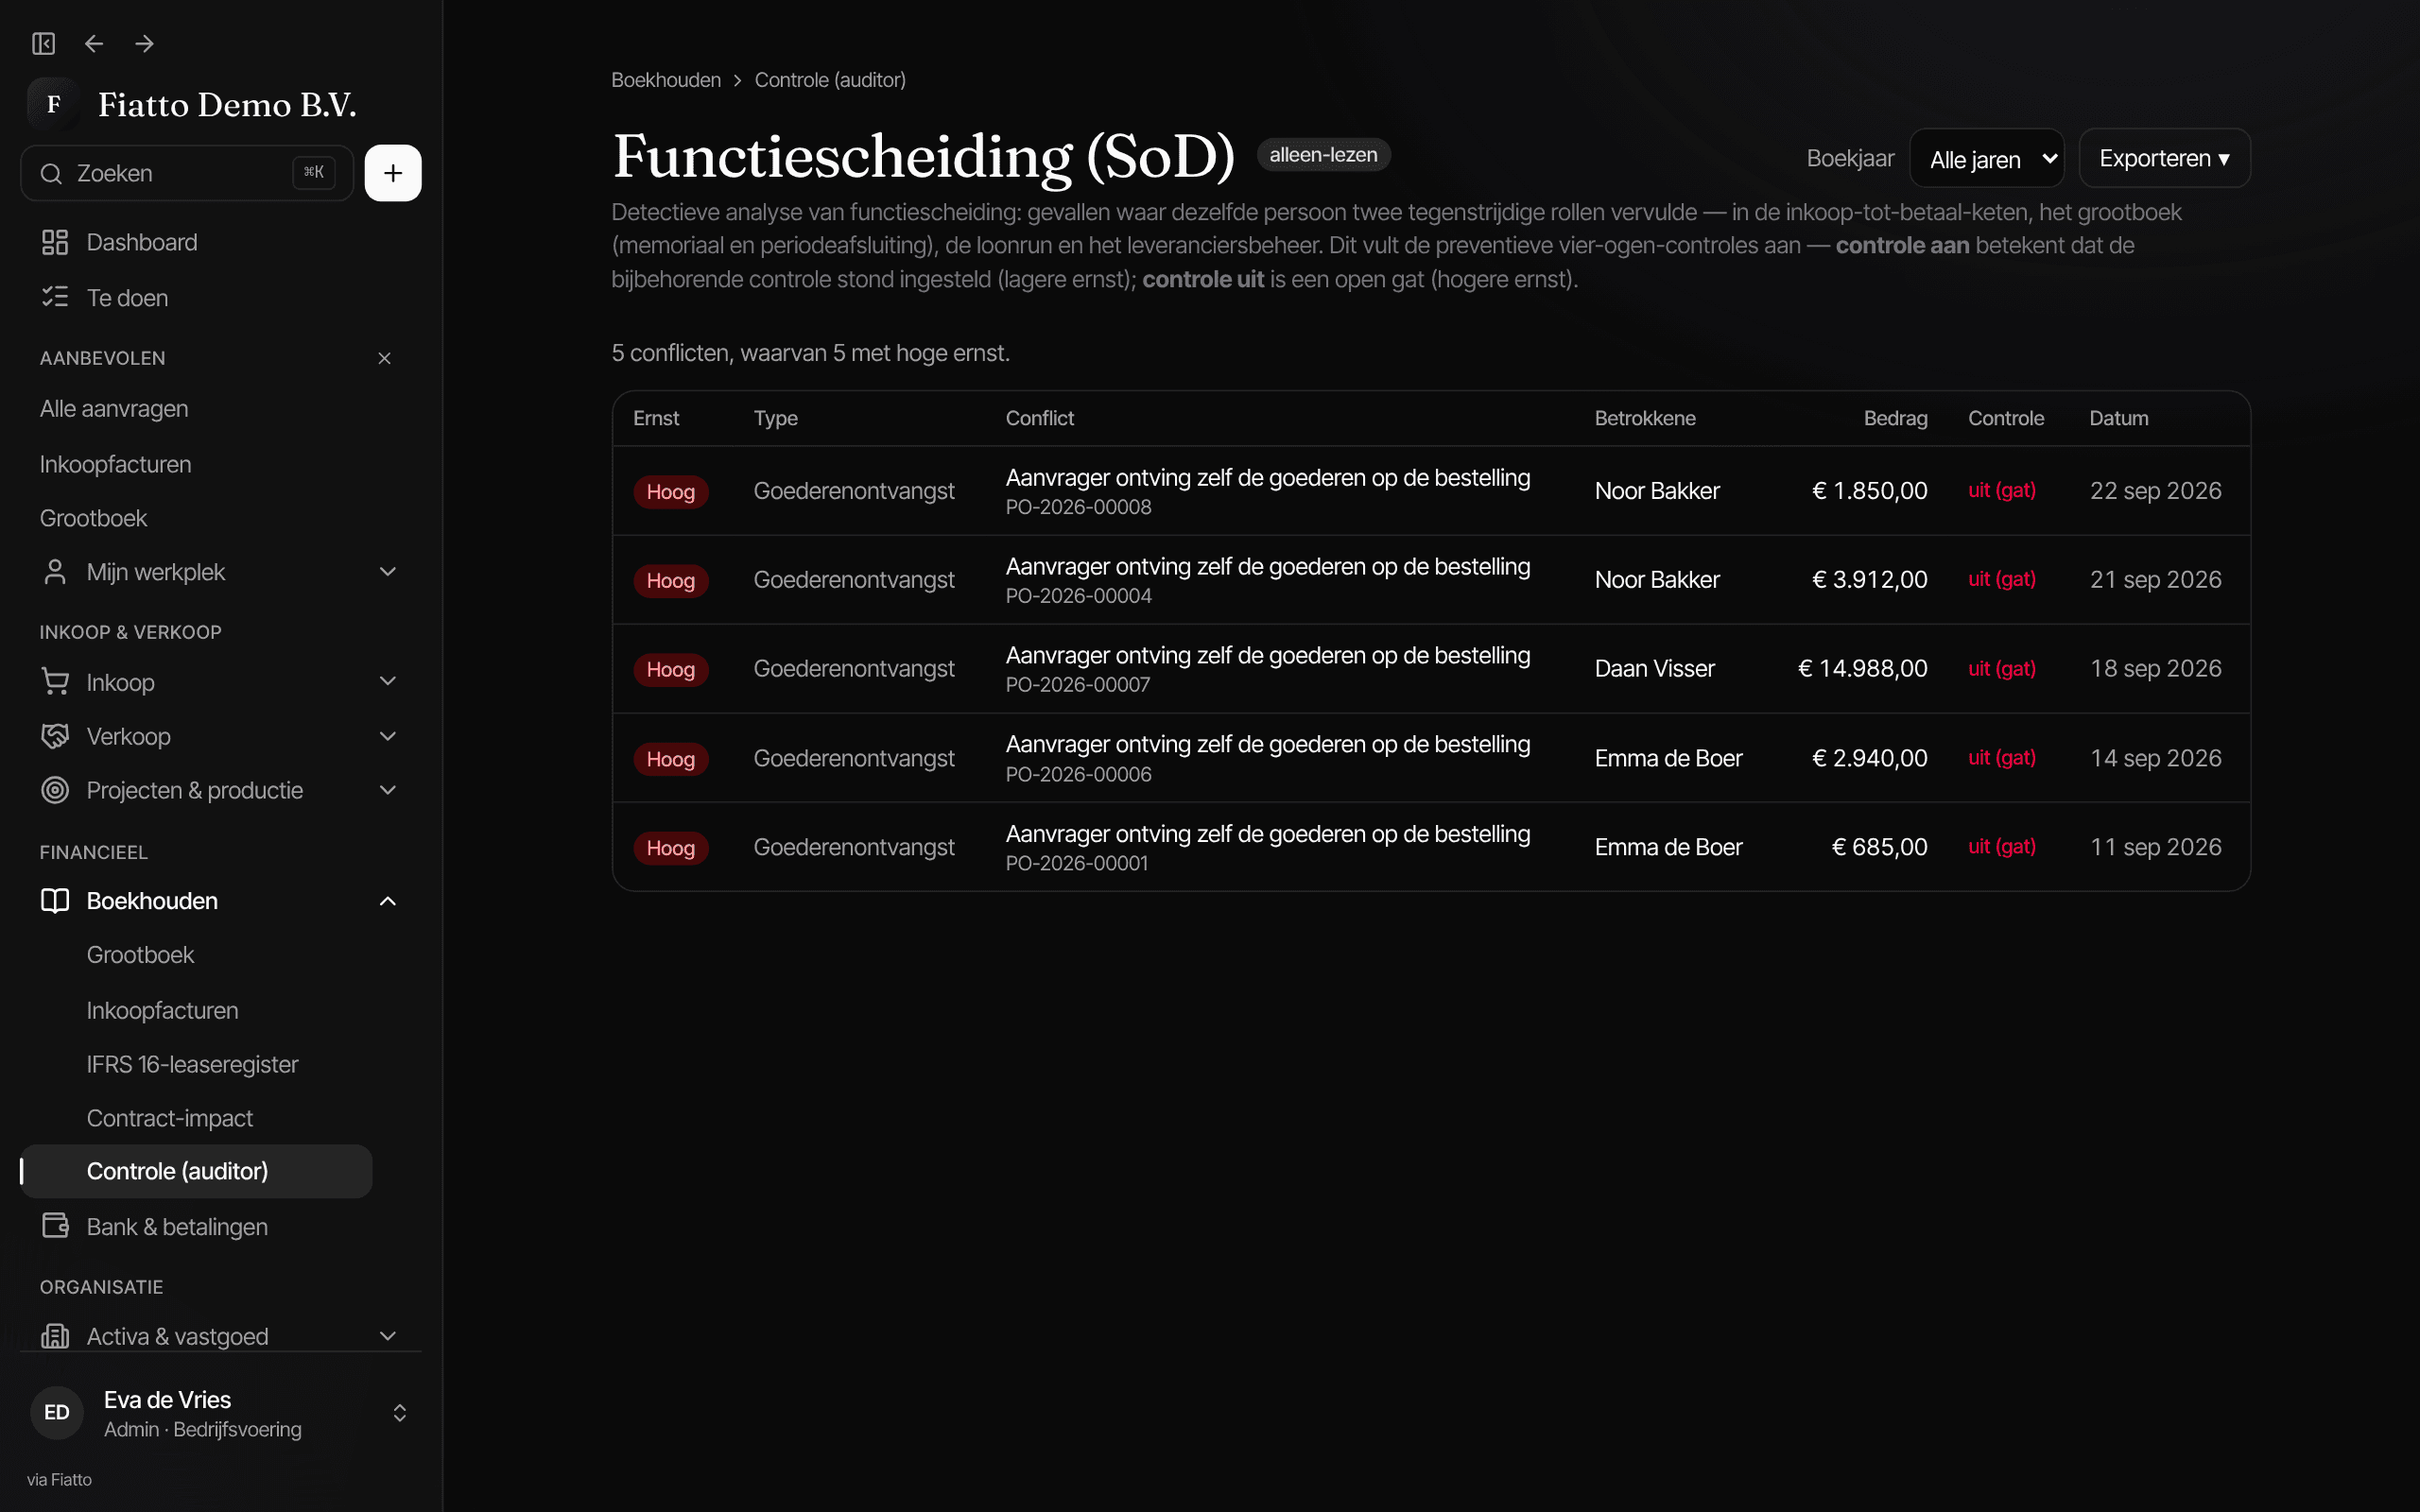
Screenshot from Fiatto, demo company with fictional data.
The problem
Most fraud runs through processes that rely on trust.
Authority isn't written down
Who may sign up to which amount lives in people's heads and emails. During holidays or turnover, someone else suddenly signs.
Too many rights with one person
The same employee creates suppliers, changes bank accounts and prepares payments.
Signals come too late
A changed IBAN or a duplicate request only surfaces at the audit, when the money is already gone.
Three layers of control
Controls built into the chain, not into a separate checklist.
Example · fictitious data
1 · Who may decide
A delegation-of-authority matrix with stand-ins
For each role and amount it is fixed who may approve; above the threshold two people sign. When someone is away, a designated stand-in approves temporarily, and that is in the audit trail too.
2 · Who can do what
Segregation of duties (SoD) reviewed
Fiatto shows which combinations of permissions in the purchasing chain are risky and with whom they currently coincide. Each conflict becomes a card in the action centre, so you resolve it or accept it deliberately.
3 · Before release
Suspicious patterns flagged
Detectors report a bank account changed shortly before a prepared payment, catch duplicate invoices before the payment run and bundle duplicate requests. With four-eyes on bank details, a new IBAN only takes effect after a second administrator approves. The check on prepared payments uses the bank connection in Complete.
Setting up
Designed to be live in one working day, with the rules you already have.
Record the authorities
Copy your current signing authorities into the approval matrix, per role and amount.
Turn on four-eyes for bank details
A supplier's changed bank account then only takes effect after a second administrator approves.
Let the signals run
From then on, segregation-of-duties conflicts and fraud signals appear in the action centre automatically.
Questions about internal controls
Does this replace our auditor's review?
No. Fiatto makes your controls demonstrable: every approval, change and review is in an immutable audit trail, and your auditor can get a read-only audit workspace in Complete if you wish.
Does Fiatto stop payments itself?
A signal blocks nothing: it sits in the action centre with a link to the payment, and a person decides. If you want a hard gate, turn on four-eyes for bank details; a new bank account then only takes effect after a second administrator approves.
We're small; do we need segregation of duties?
Small teams are exactly where permissions tend to coincide. The analysis shows where, and four-eyes approval and stand-ins cover what you can't separate.
See where your chain is vulnerable today?
30 minutes, on your own approvals and payment process.
Next: procurement, the chain these controls live in →All modules